
MC1540348 High
Microsoft SharePoint: Data access governance report for group permissions
Summary AI-generated
SharePoint admins gain a new report to identify all sites a group can access and review potential exposure or permissions via the SharePoint admin center.
Suggested actions AI-generated
- Review current SharePoint site permissions configuration
- Notify SharePoint administrators about the new report
- Update internal documentation and workflows
Written by Azure OpenAI (gpt-4.1) from the text of the post below. It can be incomplete or wrong; the original post is authoritative.
Similar posts
Search for more like this- MC1197128 New permissions report available in SharePoint admin center
- MC1450131 Microsoft SharePoint: New report on Everyone except external users
- MC1198704 Microsoft SharePoint Online: Email customization for site access review from Data Access Governance reports
- MC1274323 SharePoint Advanced Management: Delegate management of Restricted Access Control (RAC) to site admins
- MC1259825 SharePoint Advanced Management: Site admin control for restricted content discovery
- MC1413301 New in Catalog Management: Create custom group of sites
Original post from Microsoft
[What and why]
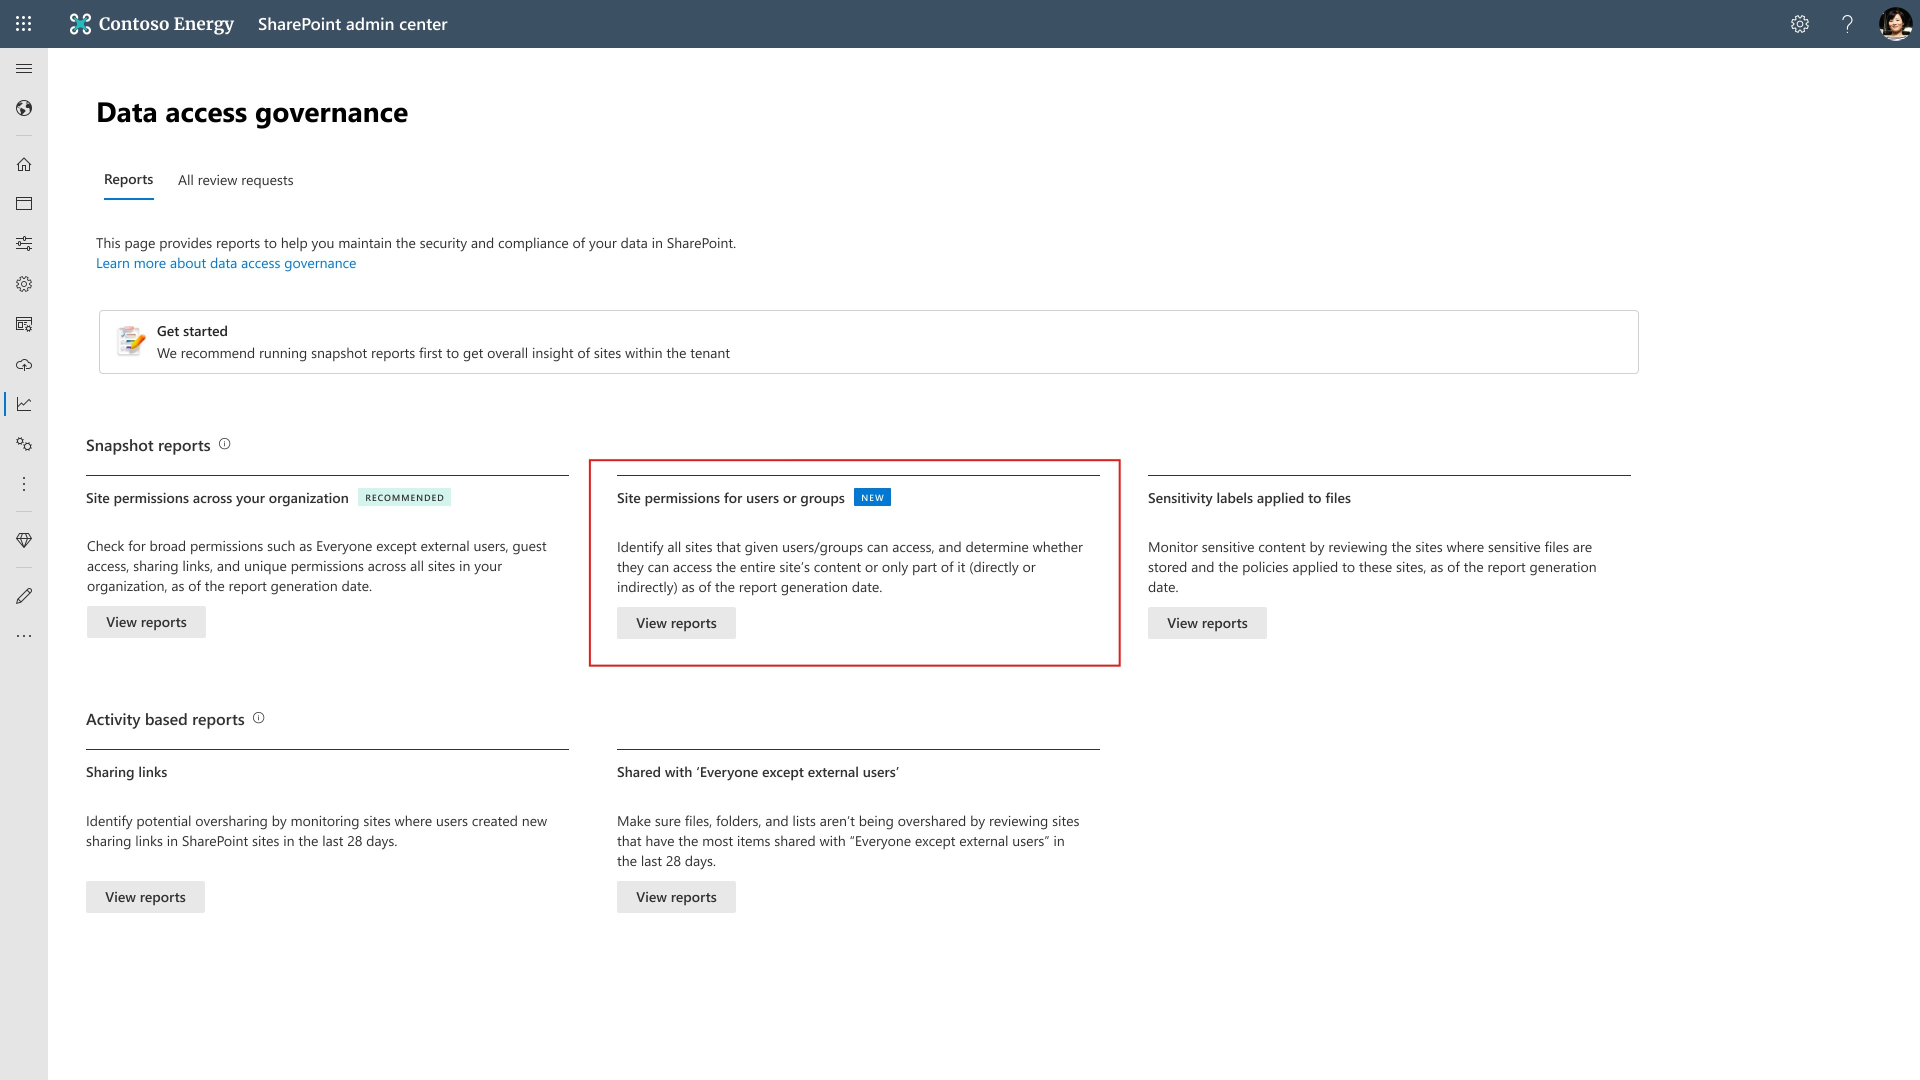
We are introducing a new Data access governance report in the SharePoint admin center that allows SharePoint administrators to identify all sites accessible to a given group and the extent of that access. Groups with broad membership, including groups created for vendors, can expose sensitive content to unintended recipients. This report helps administrators investigate potential exposure and verify group permissions.
[Rollout schedule]
- General Availability (Worldwide, GCC, GCC High, DoD): Rollout will begin in late November 2026 and is expected to complete by early December 2026.
[Impact on your organization]
Who is affected
- SharePoint administrators responsible for managing and reviewing site permissions.
Platforms and services
- Microsoft SharePoint admin center
- Data access governance
What will happen
- SharePoint administrators will be able to use the new report to identify all sites accessible to a given group. The report will show the extent of the group's access to those sites.
- Administrators can use the report to investigate potential exposure of sensitive content and to review group permissions before assigning Copilot licenses.
Data access governance page
[Action required and recommendations]
We recommend that you:
- Review your current SharePoint site permissions configuration to identify potential exposure.
- Notify your SharePoint administrators about the new reporting capability in the SharePoint admin center.
- Update your internal documentation and workflows to reflect this change.
[Learn more]
[Compliance considerations]
No compliance considerations identified. Review as appropriate for your organization.
Additional details from Microsoft
- RoadmapIds
- 561039
- Summary
- Microsoft SharePoint is introducing a Data access governance report in the admin center to help administrators identify sites accessible to specific groups and assess access levels. Rolling out worldwide from late November to early December 2026, it aids in managing permissions and preventing unintended content exposure.
- Platforms
- Web